Why Did the US Block Britain's Pre-Release AI Tests—Then Reverse Course?
A Reuters report says US developers can again give Britain's AI Security Institute early access to models. The reversal restores cooperation but exposes how fragile cross-border safety testing remains.
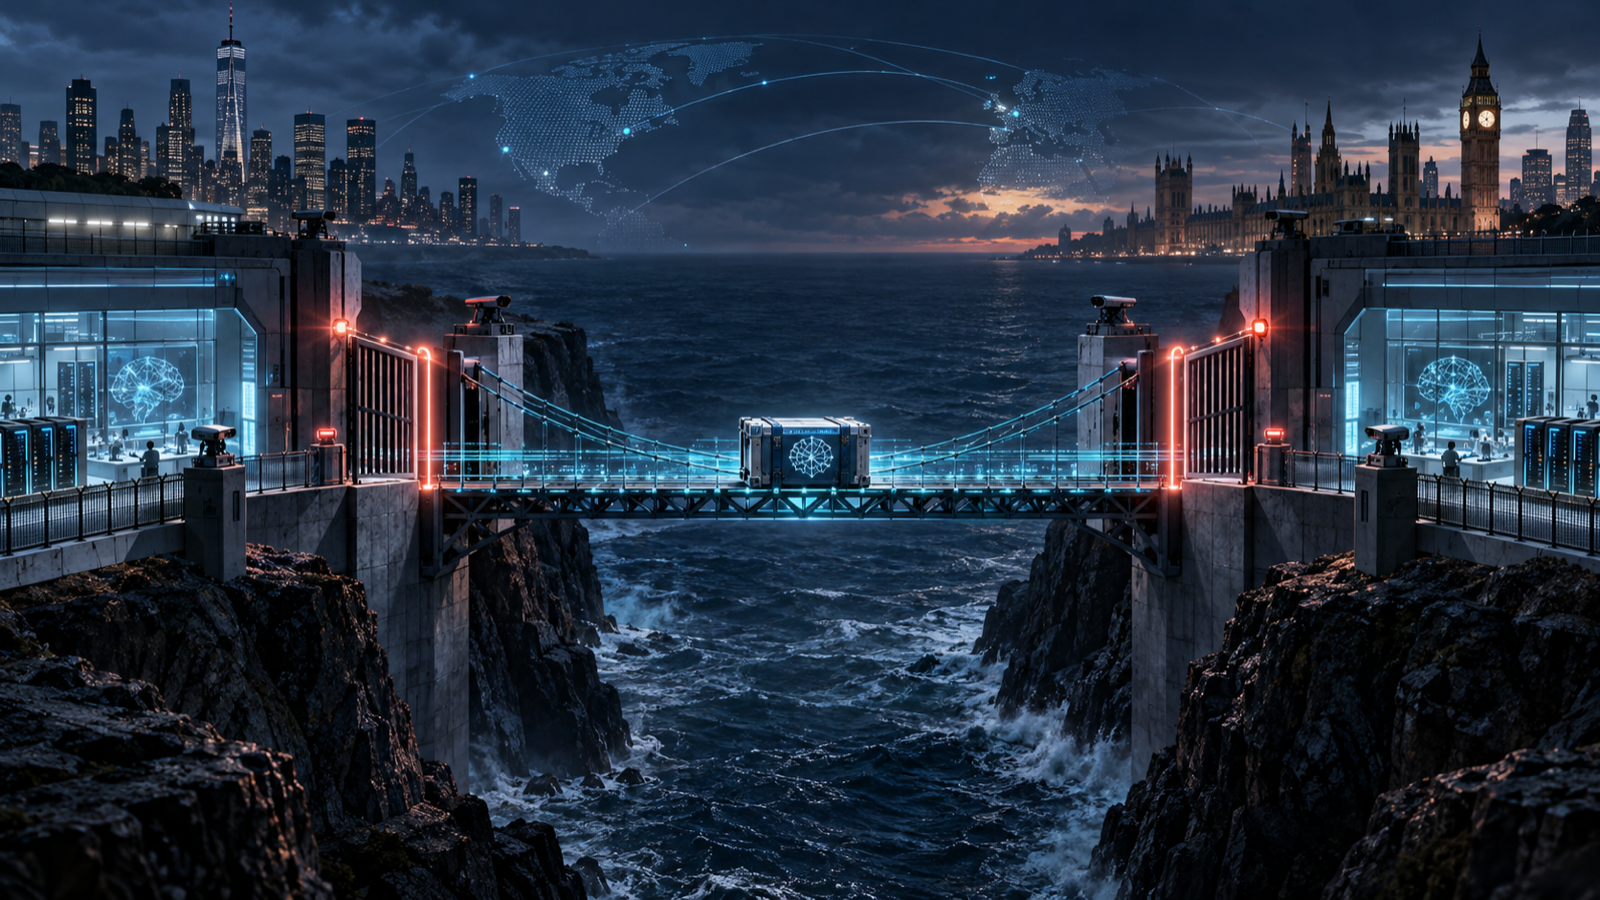
US AI developers can again give Britain’s AI Security Institute early access to advanced models for safety testing, according to a Reuters report citing the Telegraph. The reported reversal ends a short-lived request that companies including OpenAI and Anthropic avoid sharing unreleased models with the British institute.
No detailed public order accompanied the report, and the White House, OpenAI, and Anthropic had not responded to Reuters at publication time. The confirmed fact is therefore narrower than the headline: a major news service reports that the US position changed, while the precise scope and conditions remain unclear. Readers should treat the shift as a signal rather than a settled rule. A reported change in posture is not the same as a published framework, and the difference matters when the next model launch arrives and someone has to decide, in real time, whether a British evaluator gets the weights, the API, or nothing at all.
Why pre-release access matters
The most capable AI systems are difficult to evaluate after launch. Once a model is public, dangerous capabilities can spread through APIs, copied weights, integrations, and user-created tools. Pre-release testing gives evaluators time to examine cyber, biological, deception, autonomy, and misuse risks before broad access.
The mechanism is straightforward even if the practice is not. A model under development can be queried with adversarial prompts, run against benchmark suites, stress-tested on long-horizon tasks, and probed for whether it knows what it does not know. Evaluators can vary temperature, context length, and tool access to see how behavior shifts. After release, that control erodes: users discover edge cases faster than any lab can catalogue them, fine-tunes drift from the original, and downstream products inherit capabilities nobody explicitly tested. Pre-release access is the difference between inspecting a bridge before traffic arrives and counting the cracks afterward.
Britain created its AI Security Institute after the 2023 AI Safety Summit and built partnerships with frontier developers and foreign governments. Its value depends on receiving meaningful access early enough to test systems under controlled conditions. An institute that only sees finished products can describe risks; an institute that sees models before deployment can help shape them.
If access can disappear because of a political instruction, the testing framework is not independent infrastructure. It is a permission that can be withdrawn. That distinction is the heart of the episode. Infrastructure implies procedures, staffing, and expectations that persist across administrations. Permission implies a phone call, a memo, and a wait for clarification.
Why the US might restrict sharing
Pre-release models are commercially and strategically sensitive. Their behavior can reveal training methods, safety weaknesses, product timing, and capabilities relevant to national security. Governments may worry that foreign evaluators create another route for leaks or intelligence collection.
Companies also face confidentiality risks. A model shared for testing may include unreleased features, system prompts, safeguards, or deployment tools. Cross-border access requires clear rules on personnel, storage, logging, incident handling, and destruction of test artifacts. Each of those rules costs time and legal attention, and each is a place where a launch schedule can slip.
Those concerns are legitimate. But blocking cooperation entirely can weaken the evidence available to every government. Advanced model risks do not stop at national borders. A model trained in one country and deployed through a global API is, functionally, a shared object. If only the developer’s home government can inspect it early, everyone else is reasoning from press releases and public benchmarks.
There is also a competitive logic that cuts both ways. Restricting access protects domestic advantage, but it also isolates the restrictor from outside scrutiny. A safety claim tested only by the lab that made the model is weaker evidence than one replicated by an independent evaluator with different incentives. The reported reversal suggests Washington weighed that trade-off and moved, at least for now, toward openness.
What the reversal changes
The reported change gives developers more freedom to cooperate with the British institute without fearing conflict with US policy. It signals a softer stance toward international safety testing, but it does not establish a durable treaty or mandatory process.
For developers, the practical effect is legal cover. A company weighing whether to hand unreleased weights to a foreign institute no longer has to guess whether that counts as a policy violation. For the institute, the effect is restored access without a guarantee. For everyone else, the effect is a reminder of how much of the global safety architecture rests on voluntary arrangements.
Voluntary access remains vulnerable to three failures:
- A government can change its position quickly.
- A developer can limit the model, tools, or evaluation time provided.
- Evaluators may be unable to publish enough detail for independent scrutiny.
The episode shows why safety testing needs procedures that survive political cycles and product launch pressure. A framework that depends on goodwill is tested precisely when goodwill is scarcest: during a competitive launch, under deadline, with lawyers watching.
A durable model for international testing
A stronger system would define which models qualify for pre-release review, how many days evaluators receive, what tools and safeguards are included, how confidential material is protected, and which findings must be reported publicly. Thresholds matter: a small fine-tune and a frontier model should not trigger identical scrutiny. Timelines matter: an evaluator given a weekend cannot do what an evaluator given a month can. Publication rules matter: findings that stay secret cannot inform regulators, competitors, or the public.
Governments also need a mechanism for disagreements. A developer may consider a capability safe while an institute sees unacceptable risk. Without a clear escalation path, testing can become advisory theater. A defined process, with written findings, response deadlines, and an arbiter, turns a dispute into a record. Records can be reviewed; arguments cannot.
Independent replication matters too. A single institute’s result should not become unquestionable simply because it received privileged access. Multiple qualified evaluators should be able to compare findings under common security rules. Replication protects against error, but it also protects against capture, the slow drift by which an evaluator becomes too close to the industry it assesses.
None of this requires a sweeping treaty. It requires paperwork, schedules, and a willingness to be bound by them. The reported reversal is a step back toward cooperation; the harder work is turning cooperation into routine.
Verdict
Restoring US-UK cooperation is better than preventing it, but the reversal exposes a structural weakness: international AI safety testing still depends on temporary political permission and voluntary corporate access.
The real test is not whether Britain can inspect the next model. It is whether the two countries can create rules that make credible pre-release evaluation routine, secure, and resilient when governments change their minds.
Sources
> Want more like this?
Get the best AI insights delivered weekly.
By subscribing, you agree to our Privacy Policy. You can unsubscribe at any time.
> Related Articles
Control Room Can Halt Research Output in 35 Seconds—What Keeps Running?
OpenAI's Control Room puts research inference behind a central stop system. For builders, the hard question is what a stopped workload can keep doing.
OpenAI's Control Room Can Cut Off Research—What Does It Leave Running?
OpenAI's Control Room puts research inference behind a central permission check. For builders, the revealing detail is what a stop command leaves running.
Fable 5.2 and Mythos 5.2 Share a Core—So What Are You Choosing?
Anthropic's Fable 5.2 and Mythos 5.2 share an underlying system but different safeguards. For builders, the first decision is access, then the acceptance test.
Most Read
- 1 Kimi K3.1 Pro: China's Open-Weight Model Just Caught the Frontier
- 2 OpenAI Is Buying the Bottleneck: Can Orchestra Bio Cut a 15-Year Drug Timeline?
- 3 1,068 Tokens Per Second: Can Mercury 3 Change How LLMs Generate Text?
- 4 Same Price, Better Coding: How Good Is DeepSeek V4.1 Flash 1017?
- 5 Used OpenCode? Should You Rotate Your API Key After the Console Breach?





Latest News
- Decisions API Scores 1,000 Questions—Can Its Confidence Travel?
- Edge0-145B Promises Frontier AI on Your PC—Which PC?
- Hydrogen Starts at $1.50—What Will a Finished Task Really Cost?
- $0.10 per Million Tokens: Decisions API Has a Different Catch
- Control Room Can Halt Research Output in 35 Seconds—What Keeps Running?
- Huawei Released MACaQ—Will Its Quantizer Fit Your Local Stack?
Tags
> Stay in the loop
Weekly AI tools & insights.